Planning the Infrastructure That Powers the Modern Guest Experience
In this series, we address how hospitality properties can plan, deploy, and support technology that shapes the modern guest experience. In Part 1, we focus on the infrastructure that makes guest-facing technology possible. Part 2 will explore how WorldVue works with properties to design, install, and support these systems from start to finish.
Guests expect fast, reliable connectivity everywhere on a property. From streaming in the guest room to connecting devices in meeting spaces, technology now shapes the entire stay experience. But those guest-facing services only work well when teams correctly design the underlying infrastructure.
For hospitality properties, network planning should begin long before installation starts. Cabling pathways, network equipment rooms, and wireless access point placement all influence the performance of the final system. When engineering teams consider these elements early, properties can avoid unnecessary cost and disruption later.
Strong infrastructure also supports the broader ecosystem of guest-facing technology across the property. Connectivity enables streaming, casting, mobile services, and other digital experiences guests expect today.
Planning the network with these services in mind helps ensure the technology environment can grow as guest expectations evolve. As an experienced hospitality technology provider, WorldVue maintains a dedicated in-house engineering team. With this team, we can evaluate these requirements early and translate them into practical infrastructure plans.
A common challenge in hospitality projects arises when properties make technology decisions late in the construction or renovation process. By that point, building layouts and infrastructure pathways are already fixed.
Engaging a technology partner early enables hotel teams to evaluate floor plans, equipment locations, and cable pathways before finalizing construction decisions. This step can prevent inefficient design and reduce the need for expensive changes later.
“The earlier we’re involved in a project, the better the outcome for the property,” says Hitesh Patel, VP of Solution Architecture at WorldVue. “If technology planning happens after properties have already locked in construction decisions, it often leads to compromises or added cost that we could have avoided.”
Early collaboration also allows teams to plan for future technology demands rather than designing solely for current needs. Our in-house engineering team can help review architectural plans and anticipated needs. Thus, properties can align infrastructure decisions with both brand requirements and the property’s long-term technology roadmap.
A strong hospitality network begins with the physical infrastructure that supports it. That includes structured cabling, main equipment rooms, and intermediate telecom closets throughout the property.
The location of these rooms matters. Network cabling has distance limits, so poorly placed closets may require additional equipment rooms and extra fiber connections.
“Sometimes a small change in where the main telecom room sits can eliminate the need for multiple additional closets,” Patel explains. “That can save both equipment cost and installation complexity.”
Careful planning also ensures there are clear pathways for cabling between floors and across the property. Elevators, utility spaces, and other vertical pathways often play an important role in efficient network design.
Planning these pathways during construction is far easier than retrofitting them later. Guidance, such as that outlined in WorldVue’s hotel technology planning guide, can help hoteliers avoid common design challenges.
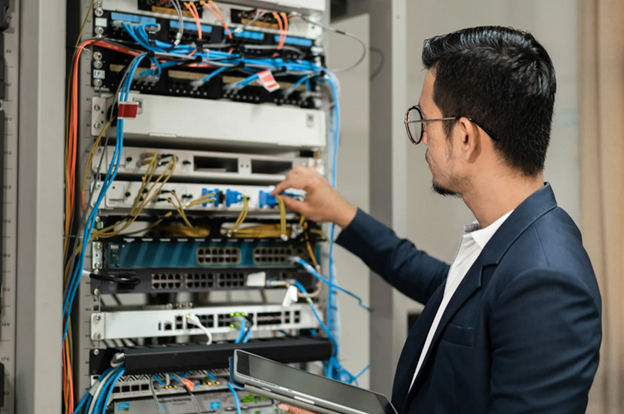
Technology infrastructure in hospitality must also align with brand standards. Many major hotel brands specify approved vendors for network hardware such as access points, switches, and other core components. These standards help ensure consistent performance and security across properties.
When brands define required equipment, those standards guide the technology design from the start. For midscale brands and independent properties, owners may have more flexibility in equipment selection.
In those environments, experienced engineering teams can evaluate the building layout, expected guest usage, and operational needs to recommend equipment from leading technology vendors. The goal is always to deliver reliable performance while meeting the property’s specific requirements.
WorldVue works with a wide ecosystem of technology partners. This helps ensure each property receives equipment suited to its needs.
Wireless connectivity depends heavily on the placement of access points. The goal is not simply to install more devices. Instead, teams must design the network to deliver strong, consistent coverage throughout guest rooms and common areas.
Construction materials can make a major difference. Signals travel more easily through drywall than through concrete or other dense materials. In some buildings, corridor access points may provide sufficient coverage. In other cases, installers may need to place access points in individual guest rooms to ensure reliable connectivity.
“Every building is different,” Patel notes. “Sometimes you can place access points in the hallway. In other situations, especially when construction materials block signals, the best option is to place them inside the rooms.” He offers an example in which the wiring is in the hallway’s drop ceiling, with APs above the doors in each room.
Engineering teams must balance signal strength with practical considerations such as cabling availability and installation complexity. The right approach depends on each property’s structure.
Every hospitality property presents its own design challenges. Some buildings have multiple towers or large campuses. Others may be historic structures with limited traditional cabling pathways.
In these situations, infrastructure design often requires creative solutions. Technology teams may need to identify alternative pathways, surface-mounted cabling, or specialized equipment. During the design process, our in-house team considers both operational and aesthetic requirements.
“We’ve worked with properties where you simply cannot run traditional cabling behind walls,” Patel says. “In those cases, the design has to adapt to the building while still delivering the performance guests expect.”
With the right planning, even complex environments can support high-performance connectivity. This applies to everything from a 100-room midscale hotel to a multi-building luxury resort.
Connectivity is the foundation for many of the technologies hotel guests interact with during their stay. Streaming entertainment, casting, property apps, and other digital amenities all depend on a reliable network.
That is why hoteliers should view network infrastructure planning as a strategic decision rather than a simple installation project. When designed correctly, the network becomes the backbone that supports the entire guest technology environment across the property.
Working with a technology partner that understands the full guest technology ecosystem can also simplify planning. Coordinating multiple vendors for different systems can be difficult and costly. Instead, properties can work with a single partner that designs infrastructure with every guest-facing technology in mind. This makes it easier to align network planning with streaming, casting, and other guest services from the beginning.
Infrastructure planning is only the first step in building a strong technology environment for hospitality properties.
In Part 2 of this series, we will explore how WorldVue works with hospitality properties as a consultative partner. We will look at the company’s in-house engineering team and its approach to technology design and deployment. We’ll also address how our team supports guest-facing technology across many hotel brands and property types.
Early technology planning helps hospitality properties avoid costly redesigns while delivering the connectivity guests expect. Learn how WorldVue supports hotels with infrastructure planning and guest-facing technology solutions.
Next-generation wireless infrastructure from RUCKUS, optimized by AI, sets new standard for fan experience and stadium connectivity
Los Angeles Football Club and RUCKUS Networks Deploy Next-Generation Wi-Fi 7 Network at BMO Stadium
Next-generation wireless infrastructure from RUCKUS, optimized by AI, sets new standard for fan experience and stadium connectivity
Richardson, TX, March 3, 2026 – Vistance Networks (NASDAQ: VISN), a global provider of intelligent network solutions, announced that its RUCKUS® Networks business, in collaboration with the Los Angeles Football Club (LAFC), has completed the deployment of a next-generation Wi-Fi 7 network at BMO Stadium. This early industry installation for Major League Soccer (MLS) establishes a new benchmark for high-density wireless connectivity in sports venues, designed to elevate every facet of the fan journey.
“From day one, our vision at BMO Stadium has been to merge world-class sport with world-class technology. Selecting RUCKUS to build the first Wi-Fi 7 network in MLS was a strategic decision to extend our leadership on and off the pitch,” said Christian Lau, CTO, LAFC. “Having partnered with RUCKUS since 2018, we trust their expertise in delivering robust, innovative infrastructure. This network is the backbone for our entire digital ecosystem—ensuring seamless experiences from mobile ticketing and concessions to immersive fan engagement for every one of our 22,000 guests.”
The BMO Stadium deployment leverages a strategic mix of RUCKUS Wi-Fi 7 Access Points (APs), including the high-performance T670 for under-seat coverage and the T670SN with hyper-directional antenna technology for precise, high-density targeting in concourses and club spaces. This architecture provides blanket, high-speed coverage capable of supporting thousands of concurrent connections.
The network is autonomously managed and optimized by the RUCKUS AI™ platform, an intelligent management and assurance solution that provides real-time analytics, predictive issue resolution, and dynamic optimization for the complex stadium environment. RUCKUS Professional Services orchestrated the seamless integration of the new Wi-Fi 7 infrastructure with the venue’s existing network systems.
“LAFC consistently pushes the boundaries of what’s possible in sports venue technology. Partnering with them to deliver this landmark Wi-Fi 7 deployment is a testament to our shared commitment to innovation and exceptional fan experiences,” said Bart Giordano, SVP and president, RUCKUS Networks. “This installation isn’t just about faster Wi-Fi; it’s about providing a reliable, enterprise-grade digital foundation that LAFC can build upon for years to come—powering new applications and revenue opportunities that engage a new generation of fans.”
—END—
Vistance Networks, Ruckus Networks and their logos are trademarks of Vistance Networks, Inc. and/or its affiliates in the U.S. and other countries. For additional trademark information see https://www.vistancenetworks.com. All other product names, trademarks and registered trademarks are property of their respective owners.
For more information on RUCKUS Wi-Fi 7 solutions and the AI-driven RUCKUS AI Management and Assurance Platform, visit: www.ruckusnetworks.com/solutions/wi-fi-7
About Vistance Networks
Vistance Networks (NASDAQ: VISN) shapes the future of communications technology, pushing past what is possible. We deliver solutions that bring reliability and performance to a world always in motion. Our global team of innovators and employees are trusted advisors who listen to customers first, then deliver value. Discover more at www.vistancenetworks.com.
About RUCKUS Networks
RUCKUS Networks, a Vistance Networks (NASDAQ: VISN) business, delivers purpose-driven enterprise networks that enable superior business outcomes in demanding environments. Our solutions combine AI-powered automation, proactive network assurance, and context-aware security, providing exceptional performance with simplified management. Discover more at www.ruckusnetworks.com.
About the Los Angeles Football Club (LAFC)
The Los Angeles Football Club (LAFC) is a first-division professional soccer club and stadium events business that has redefined what a modern sports franchise can be. Since 2018, the Club has won four major domestic trophies—including the 2022 MLS Cup, two Supporters’ Shields, and the 2024 U.S. Open Cup—while becoming the first in league history to surpass $1 billion in valuation. LAFC operates BMO Stadium, one of the world’s top-grossing concert venues, and has built a global brand through a data-driven commercial model, a deep commitment to community impact, and a diverse ownership group rooted in entertainment, technology, and Los Angeles itself. LAFC is committed to uniting the world’s city through the world’s game.
Enea brings a wealth of software and expertise, spanning both the 3GPP ecosystem and Carrier Wi-Fi. Our goal is to enhance the Wi-Fi offloading solution to improve on QoE-based decisions to always ensure that the user device selects the best available network across cellular and Wi-Fi networks, all while keeping the mobile operator firmly in control. While it’s still early in the process, we’re eager to share our ideas and would love to hear your feedback. Feel free to reach out to us through this form.
We believe the market needs a pragmatic solution. Here are some problems we aim to solve:
In our companion white paper, Wi-Fi offloading – Why?, we suggest that mobile operators adopt selective offloading by deploying Wi-Fi only where it’s needed for indoor coverage and additional capacity. Now, taking this a step further, we propose making Wi-Fi offloading dynamic through a more intelligent network selection.

As discussed in the The Device is King insights post, the decision of connecting to a Wi-Fi network is in the hands of the device. A prerequisite for Intelligent Selective Offloading is to find a way to occasionally prevent the device from connecting without affecting its willingness to do so the next time. We have found a way to achieve this.
A first ambition is to prevent the device from automatically connecting to the MNO controlled Wi-Fi network if the quality and performance of the cellular session is already considered to be good. This means offloading will only occur when it clearly benefits the user, optimizing the overall network performance and maintaining a high quality of experience (QoE).
As a next step, we also aim to incorporate real-time quality data from the Wi-Fi network, allowing us to dynamically evaluate both cellular and Wi-Fi network performance. Using frequent Change of Authorization (CoA) requests, we can ensure that users are always connected to the network offering the best experience. Ideally, the Wi-Fi quality information would be provided during the authorization process and continuosly updated throughout the session.
Many Wi-Fi equipment vendors support signaling connection-related information using the RADIUS Connect-Info attribute (#77) defined in RFC2869. Some vendors have also extended this approach to include information about the Received Signal Strength Indication and Wi-Fi Channel Numbers. A challenge is that vendors have defined their own syntax for encoding the attribute’s quality information. There is ongoing work within the Wireless Broadband Alliance (WBA) to formalize the syntax for encoding the Wi-Fi quality information. If this is broadly implemented by Wi-Fi vendors, it will pave the way for a fully standardized way of providing Wi-Fi quality information to Wi-Fi service management systems such as the Enea Aptilo SMP. We are also able to extract performance KPI data via proprietary Wi-Fi vendor APIs if available.
Peak occupancy drives revenue. It can also expose weaknesses in your network.
When Wi-Fi performance drops during sold-out nights, the impact goes beyond speed tests. It affects the guest experience, online reviews, brand perception, and the likelihood of repeat stays.
When every room is booked, hundreds of devices compete for bandwidth. Guests stream video, join virtual meetings, scroll social media, and upload content at the same time.
If your infrastructure is not designed for those spikes, performance drops quickly. Slow speeds and buffering soon turn into front desk complaints.
Technology-driven amenities continue to shape guest satisfaction. A 2025 Hotel Dive report found that technology-related amenities influence how guests evaluate their stay. When connectivity supporting those amenities underperforms, the overall perception of the property can decline.
Bandwidth management during peak occupancy is about control, not just capacity.
Adding more internet speed alone will not solve the problem. You need intelligent distribution backed by proactive oversight.
Device counts per room continue to rise. Many travelers connect three to five devices during a stay. In fact, it’s not uncommon to find double that number of devices in a room. Smartphones, laptops, tablets, and streaming devices all draw from the same shared pool of bandwidth.
At full occupancy, even a well-designed network can become strained if traffic is unmanaged. A few heavy users streaming high-definition content can consume significant bandwidth. Multiply that across multiple rooms, and congestion builds fast.
The problem is rarely just due to the size of your internet pipe. The issue is how the network shares that bandwidth across users, networked devices, and applications.
A strong bandwidth strategy combines intelligent traffic control with expert network oversight. Hotels that rely on unmanaged or lightly supported systems often struggle during peak occupancy because no one is actively optimizing performance.
A managed network goes beyond installing access points and increasing internet speed. It includes specialized design, continuous monitoring, performance tuning, and dedicated support.
With a hospitality-focused managed network:
This level of oversight is especially important at peak occupancy, when device counts surge and usage patterns change quickly.
Interested in a deeper look at how managed network services compare to do-it-yourself IT models? Take a look at WorldVue’s analysis of the hidden operational and financial costs many hotels overlook.
Traffic shaping is a core component of smart bandwidth management. It prioritizes essential traffic and distributes bandwidth evenly across users and devices. This approach allows properties to:
Guests still enjoy strong performance for everyday use. At the same time, the network prevents a small number of users from overwhelming shared capacity.
This becomes especially important in hotels with meeting space. Conferences and group events can create sudden surges in demand. Without shaping policies, those spikes can affect the entire property.
Reactive troubleshooting is costly and disruptive. By the time guests report slow Wi-Fi, the experience has already suffered.
Managed Wi-Fi environments rely on proactive network monitoring tools. These tools track throughput, device density, latency, and performance trends across access points in real time. When the system detects strain, adjustments can happen automatically.
The right managed Wi-Fi solution can rebalance bandwidth allocations when needed. It can limit non-essential traffic, preventing individual users from overwhelming the network. Technical teams can receive alerts before congestion becomes visible to guests.
In this way, proactive network monitoring protects the guest experience by resolving issues before they turn into complaints. This approach protects satisfaction scores and reduces operational stress on staff.
Traffic shaping is not a substitute for proper capacity planning.
Properties should size their internet service based on realistic peak conditions, not average occupancy. Planning should account for:
If your hotel regularly reaches 90-100% occupancy, you should treat that level as standard operating conditions.
Modern Wi-Fi standards improve performance in high-density environments. However, successful performance at scale requires thoughtful design, segmentation, and continuous oversight.
WorldVue addresses this through our approach to network modernization and managed services. We focus on density planning and proactive monitoring to support peak demand scenarios.
Hardware alone cannot solve congestion. Without policy controls and continuous oversight, even advanced access points can become overloaded. Our team incorporates these aspects into your customized network design.
If you notice performance issues primarily during high occupancy, distribution is likely the root cause.
Common warning signs include:
These patterns suggest the need for smarter bandwidth control rather than simply more speed.
Reliable connectivity is no longer a premium amenity. Guests view it as essential infrastructure, and it plays a central role in shaping the overall guest experience.
When performance remains stable at full occupancy:
A managed network with traffic shaping and proactive monitoring ensures bandwidth is distributed fairly. It keeps guests online even at peak occupancy. Real-time adjustments prevent congestion before it affects the stay.
Peak nights should strengthen your reputation, not put it at risk.
If your property experiences slowdowns during high occupancy, it may be time to reassess how you monitor and manage bandwidth. Explore how WorldVue supports high-density hospitality environments through managed connectivity services.
WorldVue designs and supports hospitality networks built for high-density environments. Connect with our team to evaluate your current infrastructure and prepare for your next sold-out weekend with confidence. Outside the US, contact our international team.
For retail teams, the challenge usually isn’t “getting people in the door.” It’s turning traffic into measurable outcomes: better staffing decisions, better in-store experiences, and more repeat visits.
GoZone’s Smart WiFi platform helps retailers understand what’s happening in-store (and around the store), then act on it.
Whether you’re a large-format store with multiple access points or a single-location shop, the goals are similar:
Smaller and single-location retailers can use the same tools larger, multi-location retailers use—just scaled to what you need.
Presence4WiFi helps you understand traffic patterns—when shoppers arrive, how traffic changes by day/time, and how patterns shift after promotions or seasonal changes.
Why it matters: Better traffic visibility helps you plan labor, reduce bottlenecks, and justify operational decisions with data.
Retail teams often need more than “how many.” Presence4WiFi helps you understand journeys—how shoppers move through the space and what paths are most common.
Why it matters: Journeys help you evaluate:
When the cashier area gets crowded, the cost isn’t just a longer line—it’s abandoned baskets and a worse experience.
Presence4WiFi can support operational awareness by helping you detect crowding patterns and enabling alerts so store teams can respond faster.
Why it matters: Faster response helps protect conversion and customer experience during peaks.
Retail marketing is most effective when it’s timely.
With GoZone’s presence-driven capabilities, you can run Presence Ads that reach shoppers as they’re pulling into the parking lot—ideal for:
Why it matters: You’re influencing decisions at the exact moment shoppers are about to enter.
Retailers often need to move specific products, support vendor-funded promotions, and prove value to brand partners.
GoZone can help you:
Why it matters: You can turn marketing into a shared, trackable program—rather than a one-off expense.
GoZone Smart Wi‑Fi turns the Wi‑Fi login moment into a branded opt-in experience so you can grow a permission-based audience from real store traffic.
You can capture:
Why it matters: Owned audiences reduce reliance on paid ads and help drive repeat visits.
GoZone is hardware-neutral and works with 20+ major Wi‑Fi brands, so you can add marketing + analytics capabilities without a rip-and-replace.
Why it matters: You get outcomes without being held hostage by hardware hurdles.
If you want, we can outline a simple plan for your property based on:

As one of this century’s seminal communications technologies, Wi-Fi has steadily improved its performance over the past 25 years primarily by focusing on one key metric: speed. Expanded frequency bands, wider channels, higher-order modulation, more spatial streams – these advances were all designed to push peak throughput ever higher. Wi-Fi 8 is a decisive break from that pattern.
This was the conclusion shared by wireless technology experts during a recent RCR Wireless News Wi-Fi Forum I joined to explore the future of the evolving communications protocol. The panel – Wi-Fi 8 on the horizon: Will it be the connectivity fabric for the AI era?, was moderated by Rosalind Craven, Principal Analyst with Telecoms Consultancy, STL Partners, and featured Andy Davidson, Senior Director of Technology and Planning at Qualcomm; Spirent’s Principal Product Manager, Janne Linkola; Marcus Brunner, ISG F5G Vice-Chair for the European Telecoms Standards Body, ETSI; and myself, Product Marketing Manager at LitePoint.
As the panelists emphasized, Wi-Fi 8 is not about chasing data rates, its goal is to ensure wireless connections are predictable, resilient and deliver a consistently positive user experience even in the most challenging environments.
From “How Fast?” to “How Reliable?”
The motivation driving Wi-Fi 8 reflects how wireless networks are actually employed. For home, enterprise and industrial users, peak speeds are bounded by how they hold up in the real world, where dozens – or even thousands – of devices compete for airtime and require equal weight be paid to throughput and latency.

This includes more robust handling of interference, improved coordination across access points and better consistency at the edge of the cellular network. These performance imperatives address the frustrations users encounter every day: dropped calls, frozen video and unpredictable roaming behavior.
The panel reached a consensus that Wi-Fi 8’s value is most impactful when applied to high-stress use cases. These include enterprise and campus networks in addition to densely populated public venues like airports, stadiums and convention centers. In these cases, reliable roaming, congestion management and improved coexistence are essential for consistent performance. Smart home devices, immersive XR, spatial computing and cloud gaming platforms are another target category where low latency defines the user experience, while industrial automation applications demand deterministic performance and reliability to manage communications links for robotics, monitoring and safety-critical systems.

Standardization Timing and Top Challenges
As for timing, the panel aligned on a familiar pattern. Wi-Fi 8 is still in development within IEEE 802.11bn, with formal ratification expected later in the decade. Early implementations based on draft versions of the standard are likely to appear before then, followed by broader commercial adoption as certification programs mature.
This staged rollout mirrors previous Wi-Fi generations, but with one important difference: expectations are being managed more carefully. Rather than promising dramatic speed jumps, the industry is positioning Wi-Fi 8 as a foundation for long-term performance stability, especially in dense, high-reliability deployments.
Ultimately, timing will be influence by a series of recurring challenges that surfaced throughout the discussion:
Reliability and Interference: As wireless environments grow more crowded, interference is no longer an edge case, it’s the norm. Wi-Fi 8 aims to improve robustness in the presence of both Wi-Fi and non-Wi-Fi interferers, reducing performance cliffs and improving fairness across devices.
Congestion and Density: From apartment buildings to stadiums to campus-wide deployments, usage density stresses today’s networks. Wi-Fi 8 introduces mechanisms to better coordinate transmissions across access points and clients, improving aggregate performance and reducing contention.
Latency and Jitter: For applications like real-time collaboration, immersive media and industrial control, latency consistency often matters more than peak throughput. The panel highlighted key enablers for time-sensitive applications, including minimizing latency spikes and improving determinism.
Interoperability: With more complex features comes a greater risk of inconsistent implementations. Ensuring that devices from different vendors behave predictably and work together is a major focus of the standard.
Why Test Still Matters – More Than Ever
The panel reiterated that Wi-Fi 8’s improved reliability places a burden on validation in the form of wireless signal and radio testing. This remains essential to ensure that devices behave correctly across a wide range of real-world conditions, including interference, mobility, congestion and coexistence scenarios. Interoperability testing becomes especially critical as features grow more complex and user expectations rise.

At LitePoint, we believe Wi-Fi 8 is reinforcing the importance of comprehensive test strategies that extend beyond basic throughput measurements. Validating reliability, latency behavior and performance consistency across diverse scenarios is what ultimately ensures that the promise of Wi-Fi 8 pays off with a consistently excellent user experience.
More Than “Just Another Wi-Fi”
The panel’s conclusion was clear: Wi-Fi 8 is not defined by a single breakthrough feature. Its significance lies in a philosophical shift from maximizing peak performance to delivering dependable, high-quality connectivity where it matters most.
In that sense, Wi-Fi 8 represents a maturation of the technology. It acknowledges that wireless is no longer a convenience layer, but critical infrastructure. By prioritizing reliability, interoperability and experience, Wi-Fi 8 moves the industry closer to a future where wireless performance isn’t just something users can measure – it delivers an experience they can trust.
Atlanta, GA, March 02, 2026 (Zyxel Networks) — Zyxel Networks, a leader in delivering secure and AI–powered cloud networking solutions, is showcasing its comprehensive portfolio of high-performance, easy-to-manage, versatile networking solutions for internet service providers, including a new PTMP solution that delivers 1Gbps WiFi over long distances, at ISPAMERICA 2026 (booth #117), March 2-5, 2026, at the Cobb Convention Center in Atlanta.
At the newly expanded ISPAMERICA event – now encompassing fiber, wireless, and satellite ISPs – Zyxel Networks will demonstrate end-to-end solutions designed to help small-and medium-scale providers overcome spectrum congestion, expand service reach, improve service quality, and grow ARPU in rural, remote, and underserved markets.
PTMP, Redefined – The First with Concurrent 5GHz and 6GHz Links
Making its debut at ISPAMERICA 2026, Zyxel Networks’ next-generation Point-to-Multipoint (PTMP) solution redefines fixed wireless performance with the industry’s first concurrent 5GHz and 6GHz links. The FWA7 Root Plus and Leaf Plus aggregate both bands simultaneously to deliver stable, real-world MLO throughput of up to 1Gbps over distances of up to six miles, bringing fiber-like WiFi performance to areas previously out of reach.
By combining concurrent 5GHz and 6GHz operation across an extra-wide 560MHz of bandwidth, Zyxel Networks’ PTMP solution delivers 3.5x more capacity than typical single-band 6GHz PTMP offerings. This massive capacity boost enables WISPs to support more subscribers, higher-tier service plans, and bandwidth-intensive applications without compromising performance.
Seamless Redundancy and Interference Resilience in Real-World RF Conditions
Designed for real-world RF environments, Zyxel Networks’ PTMP solution provides built-in redundancy and interference resilience. With traffic dynamically steered across both 5GHz and 6GHz bands, the network maintains service continuity during DFS radar events, channel changes, or interference from neighboring signals. By leveraging the clean, AFC-coordinated 6GHz spectrum while continuing to utilize the widely deployed 5GHz band, WISPs can reduce congestion, improve stability, and deliver a consistently high-quality experience without service interruption.
New Band, New Opportunities for WISP Growth
Access to the less-crowded 6GHz spectrum opens new growth opportunities for WISPs without the cost burden of licensed bands. The unlocked capacity empowers WISPs to increase service quality and launch higher-margin gigabit services to boost revenue. Operation in the 6GHz spectrum is protected by AFC coordination, which proactively shields the band from interference, delivering the stability of licensed spectrum with the ease of unlicensed investment.
End-to-End Connectivity from a Single Trusted Partner
Beyond PTMP, Zyxel Networks is showcasing a complete portfolio that allows WISPs to flexibly adapt, scale, and diversify their networks:
Zyxel Networks also offers multi-gig LAN infrastructure, including USG FLEX 700H firewalls, XS3800 aggregation switches, XMG2230 access switches, and a 14-models WiFi 7 access point portfolio, all centrally managed through the Nebula cloud platform for simplified operations and faster growth.
“ISPAMERICA reflects how today’s WISPs are evolving beyond a single access technology,” stated David Soares, Zyxel Networks Vice President Channel Sales and Marketing North America. “With our redefined PTMP solution and complete end-to-end portfolio, we’re enabling providers to break through spectrum limitations, deliver fiber-like experiences over wireless, and scale their businesses with confidence, whether they deploy PTMP, PTP, fiber, or a hybrid approach.”
For more information about Zyxel Networks and its connectivity solutions, visit www.zyxel.com/us and follow us on Facebook, Xand LinkedIn.
With the release of Aliro 1.0, the Connectivity Standards Alliance (CSA) has taken another step in its mission to unify the smart home, this time by expanding access control across smart locks and ecosystems. Aliro is a standardized credential and communication protocol that enables devices to make access decisions, bringing true tap-to-unlock functionality to consumers. Now, instead of pulling out your phone, opening an app, waiting for it to load, and finding the unlock button, tap-to-unlock works instantly. The experience becomes faster and hassle-free, similar to using a contactless payment card. It also helps device makers accelerate development with a proven, ready-to-build platform designed for secure credentials, flexible connectivity options, and low-power performance.
Durin, Inc. is one of the first device makers to support the new application layer with the recent launch of its Durin Door Manager. The next-generation device works with existing smart locks and features the Silicon Labs MG24 wireless SoC. With the MG24, Durin can validate credentials and protect keys on a single secure wireless platform while the integrated cryptography accelerator keeps performance fast for end users.
Beyond making the smart lock user experience smoother, Aliro provides a standardized way to access digital smart wallets across brands. Previously, implementing this required separate processes for Google Wallet, Samsung Wallet, and Apple’s HomeKit/HomeKey, often resulting in added complexity and fees. With Aliro, ecosystem providers can simplify the experience for home users by letting digital keys live directly in the phone’s digital wallet. Users just tap their phones to the reader, with no need to open a separate app or go through multiple steps.
Silicon Labs is helping simplify development by integrating NFC directly into its SDK for Aliro-enabled solutions. This includes a tested and validated NFC transceiver driver, along with hardware-accelerated encryption and secure key management on all Silicon Labs Matter-enabled devices, giving developers confidence and reducing integration effort.
All tap-to-unlock and supporting features, including support for step-up authentication requirements, are included in Silicon Labs’ standard SDK release, making it possible to perform key validation and Access Document verification in a single NFC transaction. Because tap-to-unlock is a core requirement for Aliro certification, this integrated approach gives manufacturers a streamlined, secure path to compliance and a faster time-to-market.
Tap-to-unlock is the baseline requirement for Aliro certification, but our multiprotocol platform also enables true hands-free access, as with the Durin Door Manager.
Matter is foundational to hands-free access for commissioning devices, enabling advanced features like digital keys that allow access during specific windows of time. It also makes it so that homeowners don’t have to use different apps from various lock manufacturers. Until now, access control has been fragmented, requiring specific apps supplied by lock manufacturers. To unlock the front door, users are required to open the app that corresponds to the lock. Even in cases where tap-to-unlock is available, launching an app is necessary to gain access. When locks are tied to a single ecosystem, it limits the benefits for users. With Aliro, homeowners can change platforms or ecosystem providers without replacing their lock. And households that include Android users and Apple users can share the same seamless experience. That cross-ecosystem consistency and long-term flexibility are key.
Before Aliro, developers were required to engage every ecosystem provider individually, which included building separate firmware and software integrations as well as paying for access. Now, one implementation can work broadly across devices. This reduces costs for R&D and certification, and cuts time to market.
With Aliro, the security model is very similar to what people already trust for tap-to-pay. When you tap your phone to a lock, you’re using the same class of bank-grade cryptography that includes public and private keys securely stored on the device. As the NFC interaction happens, Aliro runs a rapid sequence of cryptographic checks, which consists of multiple key exchanges happening in just milliseconds. This includes five separate transactions, including verifying the credentials and proving that the device and the lock both hold the correct key pair. Only after that verification does access get granted. Being able to perform these calculations fast is required for a true tap-to-unlock experience. Silicon Labs’ Matter-enabled devices can execute Aliro’s cryptographic exchanges in milliseconds, combining optimized hardware security, low-latency NFC, and efficient wireless stacks to make tap-to-unlock feel instant.
Silicon Labs and Aliro are a good pairing because of our leadership position in advancing Matter and purpose-built hardware that accelerates encryption and decryption. This combination enables secure, low-latency authentication and access control without sacrificing power efficiency or user experience. In a market long defined by fragmented, proprietary approaches to mobile credentials and reader communication, Aliro is important. By establishing a common, secure foundation for how user devices and access points interact, the new Aliro standard reduces complexity, increases interoperability, and enables trusted access experiences that scale cleanly across ecosystems, form factors, and deployment models.
Public Wi-Fi has become a standard part of modern air travel. Whether streaming content or coordinating travel plans in real time, passengers expect to be connected at the gate, onboard the plane, and throughout their journey.
But for airlines, connectivity has grown into something far bigger than passenger convenience.
Airline networks now support a complex ecosystem that includes crew communications, terminal operations, distributed staff workflows, and an expanding digital infrastructure across global hubs. Public Wi-Fi, in many cases, sits directly adjacent to operational environments that cannot tolerate disruption.
That reality has changed what public Wi-Fi means in aviation.
For airline IT and security leaders, Wi-Fi is no longer simply a service layer. It is part of the operational fabric of aviation, and it represents one of the most visible, high-traffic, and exposed security perimeters airlines manage.
In an industry where downtime is unacceptable and disruption has immediate consequences, the goal isn’t simply to respond to cyber threats quickly. It’s to stop them before they land.
Public Wi-Fi is inherently challenging to secure. By design, it supports large numbers of users, many of whom are unknown, unmanaged, and connecting from personal devices.
Aviation adds additional layers of complexity that few other industries face.
Unlike traditional enterprise public networks, airline Wi-Fi environments:
This creates a perimeter that is always shifting, always high-volume, and difficult to segment cleanly.
To put it simply: airline public Wi-Fi never stabilizes.
A coffee shop hotspot may serve a predictable neighborhood. A hotel network may have steady guest turnover. Airline networks, by contrast, operate in motion, across geographies, under tight performance constraints, and with a user population that changes completely multiple times a day.
That is exactly what makes them attractive to attackers.
Public networks offer opportunities for phishing delivery, malicious domain access, and compromise pathways that don’t require deep penetration into airline systems on the first move. Often, the earliest step is simply getting a device to connect to unsafe infrastructure.
For additional context on why shared networks remain a persistent security risk, see why public Wi-Fi environments remain high-risk.
In aviation, the challenge is not simply that public Wi-Fi is exposed. It’s that the stakes of exposure are operational.
Aviation is a high-target industry for cybercriminals because disruption creates leverage.
Airports and airlines operate in an environment where:
Threat actors understand that even minor interruptions can scale quickly into reputational damage, regulatory scrutiny, or cascading operational impact.
Ransomware, phishing campaigns, and malicious domains don’t need direct access to baggage handling systems or crew applications to create harm. In many cases, the first step is much smaller:
From there, threats can escalate quickly, especially in environments where connectivity is distributed and always in motion.
In most industries, security teams rely heavily on downstream detection and response. Alerts trigger investigations. Incidents are remediated. Systems are restored.
In aviation, the margin for disruption is far narrower because operations depend on continuous availability across terminals, hubs, and staff networks. Reacting after malicious traffic has already entered the environment becomes an operational risk, not just a technical one.
That is why resilience in aviation requires upstream protection: blocking threats before they ever reach airline networks.
Every online interaction begins with a DNS request.
Before a passenger loads a webpage, before an onboard application connects, before malware can communicate with an external command-and-control server, a domain must resolve.
DNS is the first step in the connection chain, and that makes it one of the earliest points where risk can be reduced.
Protective DNS focuses on controlling this moment by blocking known malicious domains, suspicious newly registered infrastructure, and high-risk destinations before a connection is ever established.
For airline environments, this matters because public Wi-Fi is often the widest perimeter.
When threats are stopped at this early stage, airlines can reduce exposure across multiple layers of the aviation ecosystem, including:
Blocking malicious domains at the resolution level helps prevent:
When securing airline public Wi-Fi across distributed hubs and fleets, domain-level protection provides an early control point that complements broader security measures.
Airline networks are rarely centralized.
They span:
Security solutions that require heavy infrastructure changes or long rollout timelines often introduce operational friction. Aviation security teams cannot afford months of deployment cycles or tools that demand constant manual tuning.
This is one reason DNS-based protection has become appealing in large, distributed environments: it can often be implemented quickly and without extensive architectural disruption.
Because DNS is already part of the underlying connectivity layer, adding protective controls can be significantly lighter than deploying new hardware at every edge location.
Large enterprises have demonstrated how quickly DNS security can scale by deploying DNS security across thousands of locations quickly.
That kind of speed supports a key requirement: resilience without operational drag.
In addition to the massive span airline networks have, they also intersect with third-party connectivity providers and distributed operational environments.
Traditional approaches that rely heavily on VPN architecture or fragmented perimeter tooling often introduce latency, complexity, and administrative overhead, especially in environments already constrained by satellite performance and high traffic volume.
Security leaders need a way to maintain consistent control without adding friction to connectivity.
Protective controls at the DNS layer provide centralized visibility into domain-level activity across environments, allowing teams to enforce policy and monitor risk without creating unnecessary network sprawl.
Aviation is widely recognized as critical infrastructure, and expectations around cybersecurity reflect that designation. Airlines face increasing pressure to demonstrate resilience, auditability, and proactive risk reduction across their networks, including passenger-facing environments.
Protective DNS has also been recognized by federal agencies as a foundational control for reducing exposure to malicious domains early in the connection process. In the advisory NSA and CISA Release Cybersecurity Information on Protective DNS, the agencies outline what organizations should look for in a Protective DNS provider, reinforcing domain-level controls as a best practice for high-availability sectors.
For airline security leaders, the broader takeaway is that upstream protections can support both resilience and compliance readiness, particularly in environments where disruption carries immediate operational consequences.
Operational continuity is the priority in aviation, but passenger experience is never far behind.
Airline public Wi-Fi is one of the most visible digital touchpoints in the travel journey. When passengers connect onboard or in the terminal, they aren’t just accessing the internet, they’re interacting with the airline’s brand in real time. A network that feels unsafe, unreliable, or poorly managed can create reputational risk just as quickly as it creates technical exposure.
That visibility is part of what makes public Wi-Fi different from other security perimeters. It sits in front of customers, regulators, and staff all at once. Airlines have to account for safe browsing expectations, content controls, and the risk of passengers inadvertently accessing malicious or inappropriate destinations on shared networks.
When airline public Wi-Fi is secured effectively, the benefits extend beyond threat prevention. It also supports a safer, more consistent passenger environment, strengthens trust, and reduces the likelihood of brand-damaging incidents tied to unmanaged connectivity.
Airline public Wi-Fi is mission-critical infrastructure, connecting passengers, crew, terminals, and operational systems across a distributed environment that depends on continuous uptime.
Protecting that surface means stopping threats early in the connection process, maintaining performance across fleets and hubs, and keeping operations moving without introducing unnecessary complexity.
DNS-layer protection gives airlines the ability to reduce exposure at the earliest checkpoint, helping prevent disruption before it begins.
Learn how DNSFilter can strengthen airline public Wi-Fi across passenger and operational networks; schedule a personalized demo.
Your industrial footprint keeps expanding – more manufacturing plants, pumping stations, and power substations. But your security team isn’t growing at the same pace. Here’s what keeps CISOs awake: every new site increases your attack surface while resources stay flat.
If you’re managing OT security across multiple sites, you know this challenge. Teams spend weeks manually updating sensors with the latest firmware and threat intel in a never-ending loop. Site 12 runs the latest threat intelligence while Site 7 operates with firmware and threat intelligence that are six months old – leaving you exposed.
When the board or auditors request enterprise-wide reporting, you’re compiling spreadsheets from 30 sites – often taking weeks at a time. As the CISO, you have no aggregated view of vulnerabilities and threats, let alone the capability to stand-up an enterprise-wide governance program to drive down cyber risk strategically.
This approach isn’t sustainable – or secure.
Security teams at large industrial organizations spend significant time maintaining tools instead of remediating vulnerabilities and hunting threats. Your experienced security team should not be contending with out-of-date software, needing to troubleshoot connectivity, let alone having to manually distribute threat intelligence on a site-by-site basis – tasks that should be automated.
The business impact: regulatory fines from inconsistent security posture, operational disruptions from undetected threats, and budget overruns from inefficient resource allocation. Most critically, you can’t confidently answer stakeholder or board questions about your OT security posture because you lack consistent, enterprise-wide visibility.
Industrial organizations require five capabilities to secure operations at scale:
Traditional point solutions create more silos, manual work, and security gaps.
Cisco Cyber Vision Site Manager delivers enterprise-wide management for every Cyber Vision Center and sensor across all industrial sites from a single console. Monitor sensor health, their connectivity status, license usage in real-time.
Site Manager automates software management across your entire infrastructure. Schedule and deploy updates to all sites in hours instead of weeks. The system respects operational windows – you control update timing to avoid production disruptions.
Site Manager also automatically distributes the latest threat intelligence to your entire OT security infrastructure from one location. This ensures zero-day vulnerabilities and threats are identified consistently across all sites. No intelligence gaps. No outdated protection. Additional capabilities include secure integration of Cyber Vision Centers with Cloud security solutions such as IP address geolocation to create allow and deny-list to prohibit communication to unauthorized geolocations.
Instead of updating Cyber Vision security infrastructure manually, on a site-by-site basis, your security team can instead focus on more important tasks. Existing Cyber Vision customers get to leverage this capability as part of their existing Cyber Vision license.
Now that we’ve made it easier to manage your multisite industrial security infrastructure, how do you gain aggregated visibility from all sites to drive an enterprise-wide cyber risk governance program?
The Cyber Vision app for Splunk seamlessly enables Cyber Vision Center telemetry to be ingested into prebuilt and customizable dashboards in Splunk Enterprise – the Splunk Platform. Security analysts get a complete overview of all Cyber Vision telemetry, including focused views per sensor, operational and security overviews, vulnerabilities, asset summaries, and the ability to detect and remediate malicious activity across sites in one platform.
Pre-built dashboards provide immediate value by aggregating security telemetry from all sites into a single interface. The real power of the platform lies in customization bringing OT, IT and security together for specific use cases and personas. For example, plant managers can monitor local asset health, security teams can track cross-site vulnerability or security event comparisons and get context for faster threat detection, and executives can get a birds-eye view on operational and security data.
This transforms vulnerability management from site-by-site exercises into strategic, enterprise-wide programs. Gain comprehensive visibility into security weaknesses across all industrial assets, with prioritized risk scoring based on asset criticality, exploitability, and operational context.
The Cyber Vision application can be downloaded on Splunkbase.
These capabilities work together as an integrated approach:
Cyber Vision Site Manager handles infrastructure management – centralized deployment, automated software and threat intelligence updates, health monitoring, and troubleshooting across all sites.
Cyber Vision app for Splunk powers security operations – unified Cyber Vision telemetry aggregation, transforming industrial cyber risk management from a site-by-site exercise into a strategic, enterprise-wide OT security governance program.
Together, they deliver operational efficiency, security effectiveness, and strategic oversight. Manage industrial security infrastructure with confidence at scale, remediate vulnerabilities and threats faster, and effectively communicate cyber risk to executives and auditors.
The question isn’t whether you’ll face sophisticated OT threats – it’s whether you’ll detect them in time. As industrial connectivity increases, so does your attack surface. Manual, site-by-site security management can’t keep pace.
Multi-site industrial operations require enterprise-wide security management without enterprise-wide complexity. With centralized management and unified visibility, security teams can finally scale industrial security programs to match their operational footprint.
Ask yourself: Can you confidently answer, “What’s our OT security posture right now across all sites?” How long would it take to deploy critical updates across all sites? Is your team stuck in a never-ending deployment and management loop, or are they able to proactively resolve vulnerabilities and detect threats?
Ready to see how leading industrial organizations scale OT security? Visit cisco.com/go/OTsecurity, download the solution at-a-glance or contact a Cisco sales representative to learn more about Cyber Vision Site Manager and the Cyber Vision app for Splunk.
