Data is the currency of modern workloads, from AI to analytics and more. Based on a recent industry report, the global data center market is expected to grow to 1,008.65 billion US dollars (USD) by 2034, representing a compound annual growth rate (CAGR) of 11.24 percent from 2025 to 2034.[1] It’s no surprise then that most businesses are moving quickly to keep up with this demand by updating their servers with modern processors, memory, and storage.
If you’re one of those organizations, don’t shortchange your network infrastructure in your digital transformation journey. Today, enterprise-generated data is created and processed across both traditional centralized data centers and the cloud, which means your network adapters could become a bottleneck if they aren’t equipped to handle low-latency, distributed computing needs. Performance is no longer the only factor to consider. With so much data crossing your networking threshold, scalability, reliability, and security are paramount. And of course, you need to think about the bottom line, especially when you’re tasked to do more with less.
Taking these challenges into account, the following five key connectivity considerations, along with readily available solutions, can help you achieve your data center optimization objectives.
1. Achieving consistent, low-latency performance
Despite the rise of AI, the demand for high-performance data centers is mainly driven by other causes, including growing data volumes, increasingly complex enterprise applications, and the continued growth of cloud computing. These factors, along with ongoing digital transformation initiatives, demonstrate the need for robust infrastructure that can support demanding initiatives beyond those associated solely with advanced AI. To address these demanding workloads, you can deploy servers built on advanced CPUs, like Intel® Xeon® 6 processors. But how do you also ensure your network infrastructure is up to par?
Pairing servers built on modern processors with high-performance network adapters and efficient network protocols can help optimize quality of service (QoS) for fast, reliable Ethernet connectivity. With network adapters that excel in minimizing latency, you can ensure the consistent, reliable performance needed for your demanding applications.
Another way to boost performance is to use Remote Direct Memory Access (RDMA) to reduce work handled by the processor. RDMA over Converged Ethernet (RoCE) v2 and Internet Wide Area RDMA Protocol (iWARP) can help offload tasks from the CPU during data transfers between systems.[2]
2. Ensuring reliability and compatibility
Don’t let your networking infrastructure be the weakest link in your data center. You could deploy the most reliable servers on the market and still waste valuable time and money troubleshooting downtime if your network adapters aren’t built to keep up.
The same goes for compatibility. Network adapters that can’t interoperate with previous-generation adapters or the rest of your infrastructure can inevitably lead to more costly downtime, troubleshooting, and headaches. This is particularly true for infrastructure modernization, which can be complex and disruptive if your adapter software drivers are not compatible with your existing prior-generation devices.
A better approach would be to deploy adapters with dependable failover mechanisms and other features that help ensure your network can handle disruptions without significantly impacting business-critical workloads.
You can also save yourself hours of planning, troubleshooting, and compromising by choosing solutions that come with validation, assuring comprehensive interoperability across a broad ecosystem of servers and switches. The Intel® Ethernet E830 and E610 Controllers and Network Adapters provide those benefits because they are rigorously tested for interoperability and compatibility, with extensive conformance testing and comprehensive operating system support. Additionally, both adapters offer software drivers with backward compatibility to enable consistent deployment across product generations.
3. Improving scalability and flexibility
With the explosion of data and the rapid growth of evolving technologies like 5G Virtualized Radio Access Network (vRAN), you need a network infrastructure that can meet your needs today and into the future with scalability and flexibility. For example, if your infrastructure can’t scale efficiently, you might run into performance and latency bottlenecks as you try to roll out new applications and services. Without flexibility, you could find yourself reconfiguring and redeploying adapters every time you need to adjust your infrastructure to meet changing needs.
Consider the flexibility and cost savings offered by the higher port density of the Intel Ethernet family of controllers and network adapters. For example, the Intel Ethernet E830 Network Adapter offers a wide variety of configuration choices, including 1 x 200 gigabit Ethernet (GbE), 2 x 100GbE, 8 x 25GbE, 8 x 10GbE, 2 x 25GbE, 2 x 10GbE, and 2 x 1GbE ports in a single adapter. You can use the Ethernet Port Configuration Tool (EPCT) to reconfigure the number of ports and port speeds as often as needed without revalidation, which simplifies port management. Higher port density on one adapter reduces hardware costs compared to buying multiple lower-density adapters. That’s a big advantage over other network adapters with lower port densities and more complex management schemes.
4. Strengthening security
You could deploy the industry’s highest-performing and most flexible network adapters but still regret your decision if those adapters open the door to security breaches. Loss of data or confidential information could cost your business dearly from remediation costs, downtime, and damage to your reputation. Look for network adapters that support modern cryptographic security features and a hardware root of trust that adds resilient protection against supply-chain attacks, unauthorized access, and cyberattacks.
The Intel Ethernet E830 and E610 Controllers and Network Adapters, for example, both meet Federal Information Processing Standards (FIPS) 140-3 Level 1 requirements and support secure boot and secure firmware updates compliant with Commercial National Security Algorithm (CNSA) 1.0 to provide resilient protection against unauthorized access and cyberattacks. They also offer device and firmware attestation, which protects firmware using a verifiable certificate chain and security-enabled measurement communication to help protect businesses from supply-chain attacks.
5. Improving total cost of ownership (TCO)
Performance, power consumption, and cooling costs all add up over time. According to a Goldman Sachs report, power demand from data centers is projected to increase by 50 percent by 2027, and by as much as 165 percent by the end of the decade.[3] If your data center infrastructure doesn’t operate as an integrated, well-oiled machine, you might see your overall operating costs rise precipitously, regardless of how low your initial capital costs were.
Efficiency in data center deployments is increasingly driving down costs. Features like high port-density hardware minimize initial capital expenditures (CapEx) by requiring fewer units to achieve the same levels of connectivity. In addition, selecting components with low power consumption directly curtails ongoing operating expenses (OpEx). Robust manageability and tools such as EPCT not only streamline management but also contribute to lower OpEx. The synergy of pairing these efficient network adapters with appropriately scaled servers is key to unlocking a lower total cost of ownership (TCO).[4]
The Intel Ethernet family of controllers and network adapters helps businesses achieve their digital transformation goals by offering high performance with low-latency data transfer between systems. That means your data center is ready to take on demanding workloads without breaking a sweat.
Need flexibility? The Intel Ethernet E830 and E610 Controllers and Network Adapters offer scalable architectures, comprehensive security and manageability features, small form factors, and a broad range of port-configuration options. Intel Ethernet E830 Network Adapters, with 200 Gbps maximum throughput and broad port density that includes the unique 8 x 25GbE configuration, are ideal for optimized, higher bandwidth data-plane operations. Intel Ethernet E610 Network Adapters provide industry-leading power efficiency, the latest advancements in 10GBASE-T connectivity, and comprehensive manageability features for control plane networking.
With both adapters, you can combine flexibility, simplified management, efficiency, interoperability, and strong security to achieve exceptional performance and a lower TCO in your data center.
Navigating the complexities of data center optimization requires a holistic approach. By keeping these five key considerations at the forefront of your strategy, you can build a more agile, efficient, and cost-effective data center that not only meets your current business needs, but that also lays a strong foundation for future growth and innovation. The journey to an optimized data center is an ongoing one, but with these considerations as your guide, you’ll be well-equipped to navigate the path to success.

It is estimated that there are 20 million shipping containers in transit, right now. In 2023, approximately 2.2 billion metric tons of cargo were shipped globally in containers, with the largest cargo being able to carry more than 24,000 containers.
Container ports are engines of regional growth, gateways to unlock industrial capacity. For port operators, and the local economies that rely on them, there is economic advantage in being able to unload and distribute containers quickly and efficiently.
It is a process that has become increasingly digital. While the containers may remain unchanged, rectangular boxes made of Corten steel with a marine-grade plywood floor, their movements are now governed by robotic cranes, autonomous vehicles, optical recognition and IoT sensors.
It is not enough for port operators to boast of having deep water access, modern rail links and miles of berthing. This counts for little without a solid network infrastructure.

With an annual capacity of two million TEU, DP World Evyap is vital to the Turkish economy. Its location, on the Sea of Marmara, connecting the Black Sea to the Aegean and Mediterranean Seas, is a crucial waterway for international trade.
“Any glitch in the network can create bottlenecks,” says Gokhan Erbas, IT Director, DP World Türkiye, and the man charged with overseeing the network upgrade of one of Türkiye’s most important ports.
DP World terminals currently manage 10 percent of Türkiye’s total container throughput. DP World plans to increase capacity and extend the quayside at Evyap. A reliable pervasive wireless network is a critical first step.
The 265,000sqm site had suffered from gaps in network connectivity. This hampered efficiency and created a lack of trust in digital applications. Erbas says the wireless network upgrade was vital for efficient operations and growth.
Eliminating Connectivity Dead Zones
Today, Cisco Ultra-Reliable Wireless Backhaul (URWB) covers the site with robust dependable connectivity, eliminating dead zones and restoring faith in digital workflows. Cisco URWB enables the smooth running of the Terminal Operating System (TOS), the lifeblood of any modern port.
The Evyap TOS manages everything from vessel schedules to gate access, storage planning to documentation. In an environment where over 150+ trucks are in constant motion, even a momentary network failure could have ripple effects across the global supply chain. Thanks to Cisco URWB’s zero-packet-loss architecture and ultra-low latency, DP World Evyap now operates with uninterrupted connectivity—ensuring real-time decision-making, accelerated automation, and seamless logistics flow.
Deploying ultra-reliable connectivity in an industrial port setting was a complex challenge. DP World Evyap’s dynamic operations demanded a resilient network infrastructure capable of overcoming the industry’s toughest conditions. Dense steel container stacks caused RF signal disruptions, requiring a solution that ensured uninterrupted communication. Extreme environmental factors, including temperatures exceeding 40°C, necessitated a system designed for seamless operation in harsh conditions. High-dust and high-moisture environments further emphasized the need for an ultra-durable and future-proof wireless infrastructure.
By leveraging Cisco URWB, DP World Evyap has established a cutting-edge network that not only enhances operational efficiency but also reduces maintenance costs, strengthens security, and delivers an unparalleled user experience.
“Seamless connectivity is everything,” Erbas says. “Cisco Ultra-Reliable Wireless Backhaul means operational efficiency, stronger security, lower maintenance costs and better experience for network users.”
For Evyap – Körfez, better global connections start with better local connections.
DP World Evyap in figures

Shadow IT is quickly becoming one of the biggest blind spots in cybersecurity, especially for MSPs. As clients increasingly adopt cloud-based tools, browser extensions, and AI-powered applications, many of these services bypass traditional IT oversight. These unsanctioned tools may seem minor at first, but they can introduce serious vulnerabilities to your clients’ environments.
Think of a client’s network like an iceberg. Above the surface are the approved tools: sanctioned, monitored, and secured by you. But beneath the surface lies the bulk of the threat, made up of tools operating without visibility or approval. This is where Shadow IT hides.
With remote work, bring-your-own-device policies, and easy access to cloud software, Shadow IT is expanding rapidly. The danger? It is often invisible until something breaks.
But what exactly is Shadow IT, and why should MSPs care?
What is Meant by the Term “Shadow IT?”
Shadow IT refers to any software, hardware, or cloud-based tool that employees use without the knowledge or approval of their organization’s IT team. This includes everything from personal file-sharing accounts to AI meeting assistants or browser add-ons.
Real-world examples of Shadow IT are often introduced with good intentions. A marketing specialist might store files in a personal cloud drive for convenience. A project team could adopt a planning app to collaborate on tasks. A customer success rep may use an AI-powered notetaking tool to summarize client calls. These actions seem helpful on the surface, but they introduce tools that operate beyond IT’s protective reach.
Why does Shadow IT happen? Often, it’s because the employee needs something now and waiting on approval feels like a delay. Remote work also blurs the lines between personal and professional software. And with thousands of SaaS tools just a click away, users don’t always realize the risks of choosing the easy option.
Is Shadow IT a Threat to MSPs?
It is tempting to view Shadow IT as a user issue. But for MSPs, it’s a much larger concern. Every unapproved tool represents an area of the environment that you don’t control, yet are still expected to secure and support.
Imagine this: a client starts using a project management platform to track deliverables. Weeks later, they contact you because access is lost, and key data is missing. But you were never told about the platform in the first place. Now, you’re responsible for resolving a problem tied to a tool you didn’t provision, secure, or maintain.
This is the reality of Shadow IT. It introduces unknowns into environments where predictability is your greatest asset. Over time, unmanaged tools chip away at:
“If you don’t know what tools your client is using, how can you protect them?”
Shadow IT in cybersecurity isn’t just an internal threat, it reflects directly on the service quality, accountability, and expertise your clients expect from you.
The Real Risks of Shadow IT
Is Shadow IT always bad? Not necessarily. In fact, it often surfaces because users are trying to work around workflow blockers. They want to move faster, collaborate better, or fill a perceived gap in the toolset. But unmanaged Shadow IT presents real risk, regardless of intent.
Security Gaps
Unauthorized tools typically fall outside of patch cycles, endpoint detection, and access control policies. Many also collect telemetry or data in ways that aren’t transparent. Without knowing how a tool functions or stores information, you cannot reliably assess its threat potential.
Compliance Failures
A single file uploaded to a non-compliant cloud storage app can create a cascading issue. Regulated industries like finance, healthcare, and education are particularly vulnerable, as they must adhere to strict requirements around data handling, encryption, and auditability. If an audit uncovers usage of tools that haven’t been assessed for compliance, the client may face penalties, legal exposure, or reputational damage. Navigating cloud compliance challenges becomes even more difficult when unauthorized tools fall outside your oversight.
Operational Friction
When your support team is asked to troubleshoot an issue caused by an unfamiliar tool, resolution takes longer. Shadow IT means more time spent asking questions, diagnosing issues from scratch, and uncovering causes that could have been avoided with visibility from the start.
Financial Waste
Many clients don’t realize they are paying for multiple subscriptions that do the same thing. One department may use a sanctioned CRM while another relies on an unsanctioned one. These overlaps drain budgets and make billing, reporting, and renewals more complex than necessary.
Loss of Client Trust
When clients believe you are securing their environment, they expect total coverage. If a breach is traced back to a tool you didn’t even know was in use, you may still be held accountable. Even if the client introduced the risk, their confidence in your ability to prevent future issues can take a hit.
Shadow IT Management: How to Spot Hidden Tools
Managing Shadow IT begins with identifying it. And while many unauthorized tools stay off traditional inventory lists, they leave behind usage signals that you can detect.
Behavioral Analytics
Look for anomalies in system activity. These might include sudden increases in outbound file transfers, logins to unfamiliar platforms, or data syncing from unmanaged devices. These patterns often reveal when a new tool enters the environment without proper onboarding.
DNS Filtering
This is one of the most efficient ways to uncover Shadow IT. DNS filtering allows you to monitor domain-level traffic and detect connections to cloud services that users have not been authorized to access. This is especially helpful for browser-based tools that don’t require installations and would otherwise fly under the radar.
Regular Audits
Conduct structured software and traffic audits quarterly or monthly. Include browser extensions, encrypted outbound requests, cloud storage platforms, and mobile usage where applicable. Compare findings against your client’s list of approved tools to identify mismatches.
Pro tip: Shadow IT tools can range from simple time trackers to AI transcription bots and collaborative whiteboards. Even a seemingly helpful plugin can represent risk if it hasn’t been reviewed.
Effective Shadow IT management requires that discovery becomes a regular process, not just a response to a problem.
Shadow IT Management: Strategies to Regain Control
Once you have visibility, the next step is containment, education, and long-term prevention. The goal isn’t to punish users for trying to be efficient. It’s to provide them with a safer way to achieve their goals.
Educate Users and Clients
Shadow IT often stems from good intentions. Make clients aware of the risks and responsibilities associated with unapproved tools. Encourage their teams to reach out when a tool isn’t meeting their needs instead of finding their own workaround.
Enforce Acceptable Use Policies
Establish and maintain clear, accessible technology policies. These should outline what types of tools are permitted, how to request new solutions, and what the consequences are for bypassing protocols. Policies only work when they are communicated and reinforced regularly.
Create Tool Request Workflows
A fast, transparent process to evaluate and approve new tools reduces the likelihood of Shadow IT creeping in. Clients should know exactly how to ask for a tool and what evaluation steps it must pass before approval. This process should be lightweight and responsive.
Build a Culture of Visibility
Make software usage part of your regular QBRs. Discuss newly observed tools, identify trends across teams, and recommend consolidation where appropriate. Help your clients see visibility not as surveillance but as a path to efficiency and smarter decision-making.
Why DNS Filtering Supports These Strategies
DNS filtering acts as a checkpoint for outbound traffic, helping you identify new tools before they become entrenched in your client’s workflow. This makes it easier to catch Shadow IT early and have more productive conversations about tool usage.
7 Shadow IT Tools You Probably Overlooked
Some of the most overlooked Shadow IT tools are simple, browser-based, and widely adopted:
These tools are adopted because they are easy to use. But they also avoid the standard approval and visibility processes that MSPs rely on to protect client infrastructure. For more on how Shadow IT contributes to misconfigurations and cloud risk, see our breakdown of cybersecurity trends MSPs can’t afford to ignore.
From Risk to Relationship Builder
Shadow IT is not always malicious. It is often a signal that the current workflow, stack, or process isn’t delivering what users need. MSPs who approach it with empathy, structure, and visibility tools will win client trust and long-term retention.
When you help clients understand the risks and provide a better alternative, you’re not just solving a security problem. You’re building a stronger relationship. One where technology decisions are collaborative, strategic, and visible.
Visibility is not just a security measure. It is how you deliver the strategic value your clients expect.

Smart homes are expanding, and the next wave of growth is happening outside. Connected outdoor IoT devices aren’t just indoor devices placed farther away—they operate in much harsher conditions. Ground and water attenuation, weather fluctuations, foliage density, metal fences, gates, and parked vehicles make outdoor RF connectivity a serious challenge. This blog explores how Z-Wave Long Range (LR) enables reliable connectivity in tough environments—and how you can build for it.
Connected Outdoor IoT Introduction
As connected home expectations expand beyond four walls, smart device makers face a growing challenge—and opportunity—at the property’s edge.
Customers now want secure, reliable automation not just for thermostats and locks, but for driveways, backyards, gates, gardens, sheds, and more. The connected outdoor smart home is here, and it demands more from wireless design than ever before.
For Z-Wave developers and hardware teams, this shift introduces a distinct set of engineering requirements. You’re no longer designing for temperature-controlled, interference-light interiors. You’re dealing with long-range requirements, non-line-of-sight conditions, underground sensor placements, and environmental exposure. Add in tight power budgets, signal attenuation through dense materials like stone, soil, and foliage, and the expectation of “install and forget” battery life, and it becomes clear that not all wireless protocols are up to the task.
This is where Z-Wave Long Range (LR) shows its true strength.
Connected Outdoor IoT Is Not Just “More of Indoor”
From a network design perspective, outdoor IoT devices are not simply “indoor, but further away.” They involve fundamentally different RF conditions. A smart irrigation valve buried six inches underground doesn’t just need range—it needs signal resilience through moist soil with mineral content and water-based attenuation. A driveway sensor might sit behind a metal gate and parked vehicles, while a weather station could sit hundreds of meters away from the hub, with trees and walls in between.
And that’s before considering real-world weather cycles. Connected outdoor devices must maintain stable operation across wide temperature swings, from below freezing to high heat, while continuing to communicate reliably and conserving battery.
Power delivery is also limited. Many outdoor IoT devices are entirely battery-powered, placed in remote locations with no access to mains power, and expected to last multiple seasons—if not years—without maintenance. Frequent battery replacements aren’t just inconvenient for consumers; they’re a deal-breaker in commercial and agricultural use cases.
These challenges make it clear: connected outdoor IoT demands more than what traditional 2.4 GHz mesh protocols or Wi-Fi can offer.
Z-Wave Long Range Benefits for Outdoor IoT
Z-Wave Long Range (LR) was engineered specifically to solve these challenges—and to unlock new outdoor applications for smart home device makers. Built on the Z-Wave 700 and 800 series platforms, Z-Wave LR offers a powerful combination of:
Unlike mesh-based alternatives, Z-Wave LR supports a star topology, where devices can connect directly to the hub instead of routing through repeaters. This simplifies deployments, improves latency, and makes coverage more predictable—particularly important for perimeter sensors, gate locks, and motion detectors at the far edge of a property.
And because Z-Wave LR operates at sub-GHz frequencies, it performs better than 2.4 GHz protocols in real-world outdoor scenarios, where RF interference, water absorption, and physical obstructions degrade higher-frequency signals.
Whether you’re designing soil moisture sensors, outdoor floodlights, long-range access panels, or environmental monitors, Z-Wave LR gives you the physical layer performance to connect in conditions where other radios fail.
Take your Outdoor IoT Device from Concept to Certification with Silicon Labs
Silicon Labs works closely with the Z-Wave Alliance and ecosystem partners to offer an integrated platform for building Z-Wave LR devices, supporting faster time-to-market and long-range performance in the field.
We offer three hardware paths for your connected outdoor product roadmap:
All options are supported by the Silicon Labs Z-Wave SDK, Simplicity Studio development tools, range testing utilities, and reference designs tailored to outdoor conditions.
Your Competitive Advantage Starts at the Property Line
The outdoor smart home market is still underdeveloped compared to its indoor counterpart—but that’s exactly why it matters. Demand is rising for devices that secure and automate entire properties, and Z-Wave LR is the most robust and efficient protocol to meet that demand.
For Z-Wave device makers, this is a chance to differentiate your product line, solve hard RF problems others can’t, and enter categories where reliability and battery life are non-negotiable. From smart garden lighting to water conservation systems, there’s real business in helping homeowners and property managers gain control of what lies beyond their walls.
With Z-Wave LR and Silicon Labs, you have the tools—and the range—to build it. Explore the Connected Outdoor Application Page to learn more.

Three Zyxel products have been selected as 2025 CR5 CRN Tech Innovators Awards finalists in the SMB networking, wireless networking, and network security categories.
ANAHEIM, CA, UNITED STATES, July 14, 2025 /EINPresswire.com/ — Zyxel Networks, a leader in delivering secure, AI- and cloud-powered business and home networking solutions, announced today that CRN®, a brand of The Channel Company, has selected three Zyxel products as 2025 CR5 CRN Tech Innovators Awards finalists in the SMB networking, wireless networking, and network security categories.
These annual CRN awards spotlight innovative technology vendors in the IT channel. The finalists were selected in 33 distinct technology categories across areas such as cloud, storage, networking, and security by a panel of CRN editors after closely reviewing hundreds of vendor entries and solution provider testimonials. They select finalists based on multiple criteria, including key capabilities, uniqueness, technological ingenuity, and ability to address customer and partner technology needs.
Selected as a finalist in the SMB Networking category, CX4800-56F 48-port 10G/25G L3 Aggregation Fiber Switch with 8 100G Uplinks is a high-density 48-port Layer 3 managed switch that features upgradable SFP28 ports to support current 10GbE requirements and enables users to upgrade to 25GbE as network demands increase. Incorporating sophisticated firmware to support both on-premises and cloud-managed network requirements, CX4800-56F brings Zyxel partners forward to the next iteration of speed beyond 10G by offering 25G and 100G for aggregation and core switch needs.
WBE630S BE12300 WiFi 7 Tri-Band Dual-Radio NebulaFlex Pro Access Point, a finalist in the Wireless Networking category, offers speeds up to 12.3Gbps and delivers low latency for fast, reliable connectivity in high-traffic environments. The affordable access point features a BandFlex radio that enables it to support 2.4GHz and 5GHz or 6GHz by configuration, making it an ideal solution that can extend an existing 5GHz network while providing the flexibility to add or upgrade the network to 6GHz. Smart Antenna technology uses dual-optimized antennas that automatically adapt its antenna patterns to achieve peak performance and ensure optimal WiFi connectivity in diverse environments.
A finalist in the Network Security category, USG LITE 60AX AX6000 WiFi 6 Security Router is a high-performance, all-in-one cloud-managed router that combines blazing-fast speeds and best-in-class threat management to provide an easy-to-manage, high-speed, secure networking solution for small businesses, teleworkers, and managed service providers. Using the intuitive Zyxel Nebula Cloud Center, businesses can easily establish secure site-to-site or remote access VPN connections to provide remote workers, such as work-from-home staff or teleworkers, secure access to the main office network to increase productivity and efficiencies.
“Each of the 2025 CRN Tech Innovators Awards finalists is a standout offering that reimagines what’s possible in the IT channel,” said Jennifer Follett, VP, U.S. Content, and Executive Editor, CRN, The Channel Company. “Each creates the opportunity to build bold solutions that solve real-world challenges for end users and drive success for channel partners. We congratulate our finalists for their commitment to innovation, partner success, and customer impact, and we can’t wait to see how they continue to push technology boundaries forward.”
“We are honored to again be recognized by CRN as one of the networking industry’s innovative vendors and are particularly excited to see Zyxel solutions representing three of our core product categories,” explained David Soares, Zyxel Networks Vice President Channel Sales and Marketing North America. “This annual awards program validates Zyxel’s efforts to deliver networking solutions that deliver a critical combination of performance, versatility, ease-of-use and management, and value, that is critical to the operations and growth of small businesses, VARs, and solution providers.”
The Tech Innovators Awards finalists will be spotlighted online at crn.com/techinnovators starting July 14. Winners will be announced online on August 6 and will be featured in the August issue of CRN.
For more information about Zyxel and its connectivity solutions, visit www.zyxel.com/us and follow us on Facebook, Twitter and LinkedIn.
About Zyxel:
Zyxel Networks is a technology provider with over 30 years of experience, specializing in delivering solutions for small to medium-sized businesses and the enterprise-edge in partnership with VARs, MSPs and System Integrators. We enable network professionals to connect and protect organizations with greater ease by bringing together intuitive, scalable and secure cloud management with a complete portfolio of network devices.
About The Channel Company:
The Channel Company enables breakthrough IT channel performance with our dominant media, engaging events, expert consulting and education, and innovative marketing services and platforms. As the channel catalyst, we connect and empower technology suppliers, solution providers, and end users. Backed by more than 40 years of unequalled channel experience, we draw from our deep knowledge to envision innovative new solutions for ever-evolving challenges in the technology marketplace.
As 5G networks expand, connecting a wider variety of devices is becoming essential. Our video series, 3 for 3, provides 3 answers for 3 pressing questions about trends in wireless test. In today’s video, LitePoint’s Khushboo Kalyani focuses on a critical evolution in the world of 5G that’s set to transform the Internet of Things: 5G Reduced Capability, known as RedCap, and its evolution, eRedCap. Kalyani discusses what 5G RedCap and eRedCap are, where they fit in the IoT landscape, and their primary use cases.
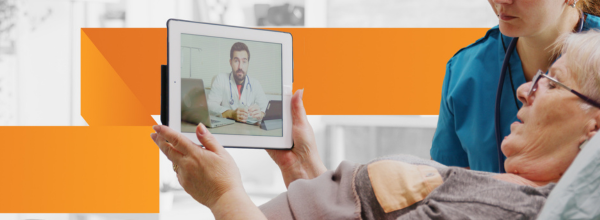
Reliable Wi-Fi® has become a must-have in senior living communities—not just for entertainment, but for residents’ safety as well as their physical and mental health. More of today’s residents are tech-savvy and expect reliable, high-speed internet like they had in their own homes. Below are the five most common Wi-Fi challenges in senior living and how RUCKUS Networks provides easy-to-deploy solutions to keep your residents and staff connected, secure, and satisfied.
Reliable Wi-Fi® has become a must-have in senior living communities—not just for entertainment, but for residents’ safety as well as their physical and mental health.
More of today’s residents are tech-savvy and expect reliable, high-speed internet like they had in their own homes. Below are the five most common Wi-Fi challenges in senior living and how RUCKUS Networks provides easy-to-deploy solutions to keep your residents and staff connected, secure, and satisfied.
Inconsistent coverage in resident rooms and common areas
Senior living facilities situated in older buildings may have thick walls or outdated infrastructure that affects Wi-Fi coverage. This can lead to frustrating buffering, frozen video or dropped connections for online access or streaming services.
Fix it with: High-performance access points (APs) that are purpose-built for dense, complex environments. RUCKUS® APs offer our BeamFlex+® adaptive antenna system capabilities that deliver property-wide reliable, seamless coverage that can even extend to outdoor areas.
Congested networks
Today’s seniors are more connected than ever: 68% of baby boomers own smartphones[1], while adults 50-plus possess an average of seven tech devices, which they use daily[2]. Unfortunately, traditional legacy networks can’t intelligently prioritize traffic or manage bandwidth effectively across hundreds of connected devices. This is especially concerning when residents are conducting a telehealth Zoom call or losing signal to their smart watch that’s monitoring them for AFib.
Fix it with: Smart traffic management and QoS controls designed for high-density environments. RUCKUS solutions support high device density and smart traffic management so networks can automatically prioritize critical applications while offering fair bandwidth distribution to all users.
Complex onboarding and access management
Providing access for residents, guests, and staff can become a logistical headache, especially when it requires manual setup or IT intervention. What’s worse is that, when private passwords are shared, revoking permission later causes a whole new basket of issues.
Fix it with: Cloud-managed networking and self-service onboarding portals. RUCKUS offers several options such as the Cloudpath® Enrollment System that enables secure, easy logins and that separate user groups to simplify administration.
Privacy and data security
In senior living environments, privacy matters. But weak Wi-Fi security, such as outdated encryption or unsecured devices, puts sensitive medical data at risk, making it vulnerable to breaches. Legacy guest devices, staff tablets, IoT sensors and facility medical systems often coexist on the same network, exposing all of them if one is compromised.
Fix it with: Our Dynamic PSK™ (pre-shared keys) and role-based access control that isolates traffic based on user type—residents, guests, staff, and IoT. Built-in security features like network segmentation, policy enforcement, and configurations help keep data secure across devices and users. This helps reduce risk and give your staff peace of mind.
Limited IT resources
Many senior living properties don’t have a dedicated IT team on-site—which means troubleshooting, setup, and updates can overwhelm staff time or cause delays.
Fix it with: Simple, centralized network management with zero touch provisioning. RUCKUS offers several cloud-based solutions that allow for remote oversight, automation, and AI-driven troubleshooting that can identify and fix issues, often before residents even notice, so your team can focus on care and not connectivity.
Smarter Wi-Fi = happier residents
Wi-Fi isn’t just about connectivity; it’s about the quality of life it offers. It not only impacts resident happiness but also staff performance, operational efficiency and even safety. Modern senior living facilities need connectivity partners who understand these unique challenges and can deliver solutions that transform Wi-Fi from a source of complaints into a competitive advantage. RUCKUS delivers a smarter, stronger, and more secure solution tailored to the unique needs of multi-dwelling senior communities.
To learn more, download our Senior Living Network Checklist or visit our Senior Living Network page.
The Internet of Things (IoT)is in the midst of a quiet revolution, and at the center of this shift is Matter. Developed by the Connectivity Standards Alliance (CSA) to streamline smart home integration, Matter has been one of the most rapidly evolving technologies in the IoT space.
What is Matter, and Why Does it Matter?
Matter is a unified application layer that abstracts the underlying transport technologies—like Wi-Fi, Thread, and Ethernet— so smart devices can communicate reliably, regardless of their network protocol. With it, developers and device makers can now build secure, interoperable products that work seamlessly across ecosystems.
In its short, lifespan, Matter has evolved from 1.0 to Matter 1.4, which now works with 54 device types including energy management devices, enhanced entertainment controls, and solar EV chargers.
Historically, HANs (home area networks) used proprietary or utility-specific protocols. But with Matter’s broad industry support and open standard approach, it’s positioned to become the default protocol for future HAN deployments, allowing energy devices to talk natively to the meter and each other.
Matter is designed to solve the biggest problem in smart homes: devices that don’t talk to each other.
With Matter:
And it’s all local, secure, and fast. No cloud dependencies. No silos. Just devices that understand each other—no matter who made them.
Think of Matter as a USB for smart homes. You plug it in, and it just works. Now imagine every energy device in your home—the EV charger, heat pump, solar inverter, and your smart meter—are all speaking Matter. They don’t just coexist, but can collaborate to save you money, shift energy usage, and make your home smarter without lifting a finger.
The Evolving Role of Smart Meters
Smart meters are no longer just energy monitors. They’re evolving into interactive nodes in the energy ecosystem, capable of:
In the near future, a smart meter will not just passively measure usage—it will coordinate with local energy-consuming and generating devices to optimize for both cost and sustainability.
Imagine an EV charger seeing a high peak price signal from your meter and delaying charging by 30 minutes to save you money—or your solar inverter exporting more power because the meter detected a TOU bonus. With more responsibility on smart meters comes the need for better communication across devices.
Ecosystems are Rallying Around Matter
If your device doesn’t support Matter, it can’t communicate or operate with other Matter-enabled devices. It’s sidelined while everything else coordinates in real time—EV chargers, HVAC systems, solar inverters, and more. You could try retrofitting it later, but that would be like trying to learn a new language after you’ve already moved abroad — you’re starting at a disadvantage.
Why Wi-Fi Is the Right Call for Smart Meters
Thread is great for things like motion sensors and door locks—low power, short bursts of communication. But smart meters are plugged in, always on, and live outside your house.
Here’s why Wi-Fi wins:
Future-Proof Your Meters with Matter Over Wi-Fi or Risk Falling Behind
We all agree that retrofitting meters in the field is a nightmare. It’s expensive, slow, and not always possible. Waiting until Matter over Wi-Fi is the new standard means you risk deploying devices that can’t speak the dominant smart home language. You’ll be stuck with meters that can’t connect to anything, and users who are stuck paying more for energy.
Silicon Labs’ SiWG917 Wi-Fi Modules are engineered specifically to deliver strong, industrial-grade, single-band 2.4 GHz Wi-Fi that is perfect for outdoor meters and built for Matter. Known for its ultra-low power performance, built-in AI/ML accelerator, robust security, and flexible architecture, the SiWG917 is the ideal choice. To learn more about the power saving features of the SiWx917, read our whitepaper, Achieve Ultimate Energy Efficiency for Low-Power Wi-Fi.
Don’t let your meter be an outsider.
Build it with Wi-Fi.
Build it with Matter.
Build it ready for the world it’s about to enter.
Smart meters need to join in, not just watch from the sidelines. Wi-Fi gives them a seat at the table, and Matter makes sure they can talk to everyone.
So don’t play catch-up in two years. Get started today by visiting our Matter Developer Journey.
The electric grid is the backbone of our modern society here in North America. Ensuring its reliability and security is paramount, which is where the North American Electric Reliability Corporation (NERC) Critical Infrastructure Protection (CIP) standards come in. These standards provide a framework for securing the Bulk Electric System (BES) against cyber threats.
However, with the grid undergoing significant modernization and increased connectivity, meeting these stringent cybersecurity requirements presents a complex challenge for power utilities. More connected devices mean a larger attack surface, demanding a robust and phased approach to security.
Cisco’s Phased Approach to Industrial Threat Defense
Cisco recognizes that enhancing your security posture is a journey. We advocate for a phased approach, building foundational security elements that support subsequent steps, allowing utilities to improve security at their own pace while demonstrating value. The Cisco Industrial Threat Defense solution offers a modular and comprehensive set of capabilities designed to address the unique challenges of securing operational technology (OT) environments and achieving NERC CIP compliance.
How Cisco Solutions Help Address Key NERC CIP Requirements:
Cisco just published a solution brief describing the key NERC CIP requirements and how our portfolio can help utilities to comply. Here is a quick summary:
A Unified Approach for Enhanced Security
Navigating NERC CIP compliance requires a strategic, solutions-based approach. Cisco provides the building blocks and integrated solutions to help power utilities secure their critical infrastructure, enhance visibility, and meet regulatory requirements effectively. Have a look at our NERC CIP Compliance Solution Brief to better understand the requirements and see how Cisco can help.
I will be presenting a webinar on July17th together with experts from Burns & McDonnell to discuss the new Internal Network Security Monitoring (INSM) CIP-015 standard and solutions available to help Utilities comply. Save the date and register now.
New partnership delivers simple and easy WireGuard VPN service to USG FLEX H Series firewall customers at no additional cost
ANAHEIM, California (June 26, 2025) Zyxel Networks, a leader in delivering secure, AI- and cloud-powered business and home networking solutions, today announced a new partnership with Tailscale, the leading identity-native connectivity platform. This integration brings simplified, scalable, and secure VPN connectivity to Zyxel Networks’ USG FLEX H Series firewalls, empowering small businesses and advanced users to build private, peer-to-peer networks with ease and at no additional cost.
Now available on Zyxel Networks USG FLEX H Series firewalls running uOS v1.32 and above, Tailscale’s WireGuard-based mesh VPN network is fully integrated into the firewall’s management interface. Once enabled, users can set up secure remote access in minutes without the need for complex configurations.
Streamlined VPN experience
The USG FLEX H Series firewalls now support a full suite of VPN protocols, including IPSec, SSL and WireGuard, to secure a wider range of use cases and endpoints. The Tailscale integration allows users to take advantage of a streamlined setup experience, which requires no server configuration or port forwarding. Devices automatically connect to the private network upon a few simple clicks, making the process accessible even to those with minimal networking experience.
Protected access control
With the Tailscale integration, firewall users can now create a peer-to-peer mesh network where devices communicate directly with each other via encrypted tunnels, instead of routing through a central server. This architecture reduces latency, boosts performance and scales efficiently as businesses grow. Furthermore, the service supports a wide range of operating systems, including Windows, macOS, Linux, iOS and Android, as well as embedded devices, and cloud services directly, allowing firewall users to extend VPN protection across all major endpoints–including mobile devices and BYOD environments.
For added convenience and security, users can log in to Tailscale using their existing identity providers such as Google Workspace, Microsoft Entra ID (Azure AD), Okta, OneLogin, or JumpCloud. Multi-Factor Authentication (MFA) can also be implemented through these accounts, providing an extra layer of protection while simplifying access control and user management.
“VPNs are essential for protecting data and supporting hybrid workforces, but they have often been too complex for smaller organizations with limited IT resources,” said Ken Tsai, President of Zyxel Networks. “This integration is the answer our customers have been asking for a simpler, faster and smarter way to enable secure connections across all their devices, wherever they are.”
“VPNs have a reputation for being slow, painful to set up, and impossible to manage. We started Tailscale to fix that, and now we’re excited to bring that simplicity to more people through our partnership with Zyxel Networks,” said Avery Pennarun, co-founder and CEO of Tailscale. “Zyxel’s reach in the SMB market means we can help a lot more teams skip the ‘VPN headache and just get back to work—securely.”
As part of the partnership’s launch, Zyxel Networks is offering eligible USG FLEX H Series customers free access to Tailscale’s Starter Plan. For more information, please visit https://community.zyxel.com/en/discussion/29583
For more information about Zyxel, its connectivity solutions, and the Zyxel Authorized Partner Program, visit www.zyxel.com/us and follow us on Facebook, X(formerly Twitter) and LinkedIn.
About Zyxel Networks
Zyxel Networks is a leading provider of secure, AI-powered cloud networking solutions for SMBs and the enterprise edge. We deliver seamless connectivity and flexible scalability through subscription services, all backed by robust security. With a reputation built on decades of unlocking potential and helping people adapt to the changing workplace, Zyxel Networks has earned the trust of over 1 million businesses across 150 markets.